EU AI Act's General-Purpose Model Rules Just Got Teeth — Fines Can Now Hit 3% of Global Revenue
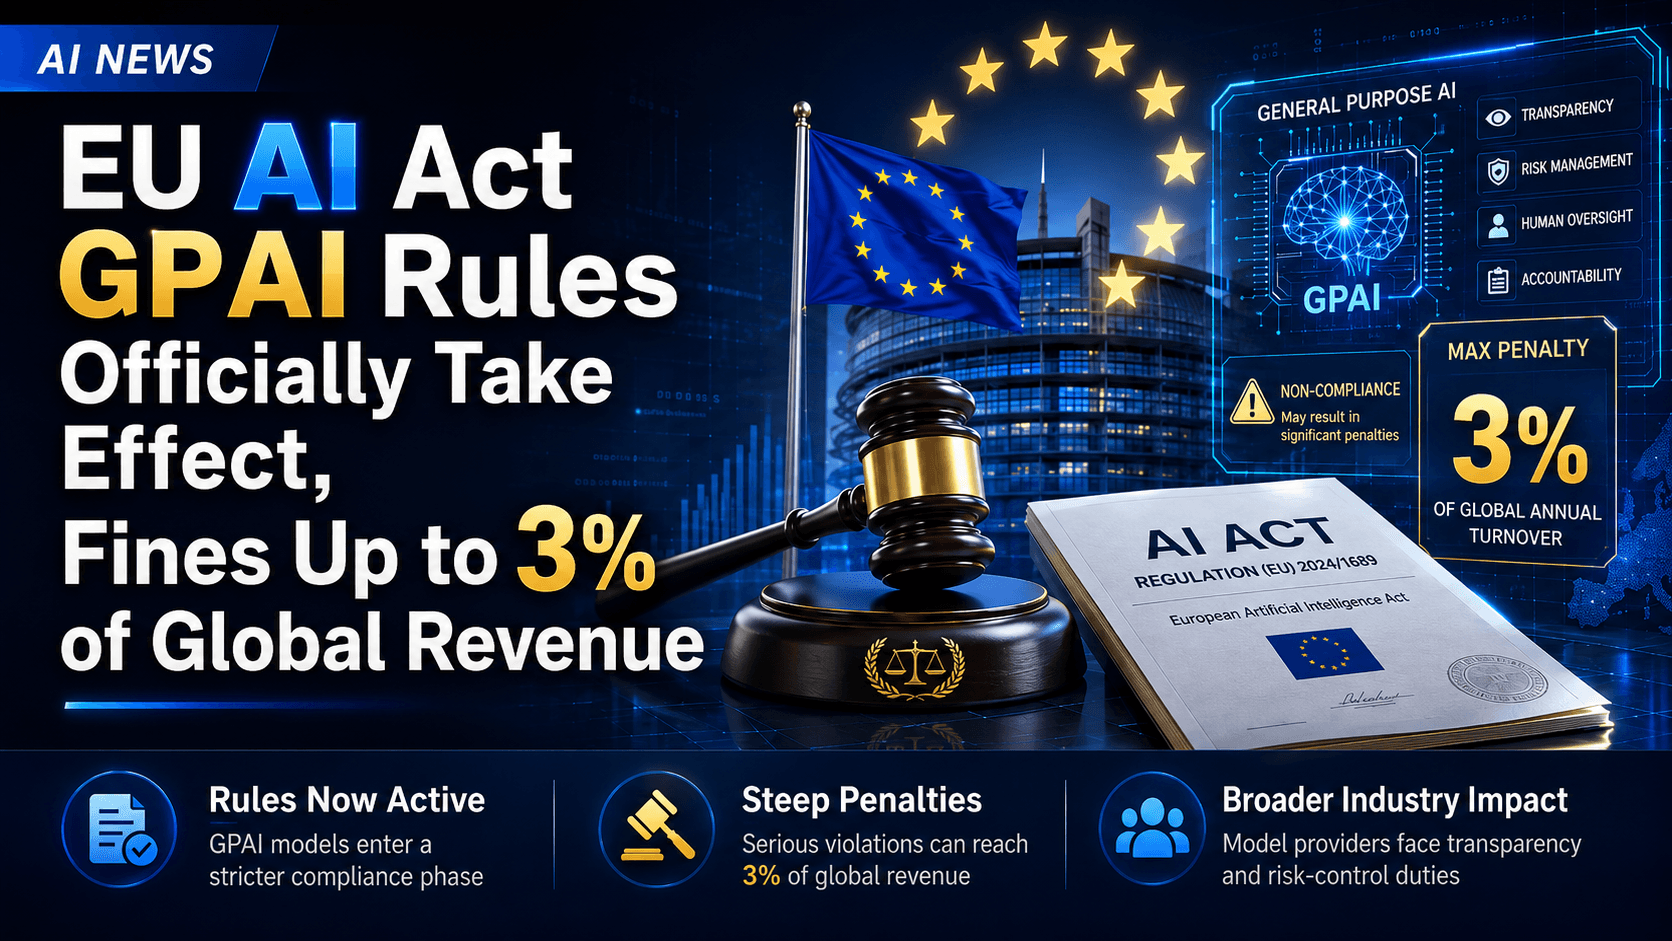
On August 2, 2026, the European Union's enforcement powers over providers of general-purpose AI (GPAI) models under the AI Act officially took effect. According to MediaLaws, this means the European Commission can now actually exercise investigative powers, demand remediation, and issue fines against major model providers like OpenAI, Google, and Meta. These obligations were written into law back in August 2025, but providers were given a full year to adjust — and now that grace period has run out.
The rules have been on the books for a year. The teeth just came in.
What Actually Changed on August 2
Specifically, according to the European Commission's own enforcement framework, the Commission now has the power to request documentation and information from model providers, conduct evaluations, demand compliance remediation or market restrictions (including product withdrawal and recall), and issue fines directly. As detailed by beam.ai, under Article 101 of the AI Act, GPAI providers found in violation can be fined up to €15 million or 3% of global annual turnover, whichever is higher. For broader violations of the Act — such as engaging in prohibited AI practices — Article 99 raises the ceiling to €35 million or 7% of global turnover.
At the core of these obligations is a transparency requirement: GPAI providers must be able to clearly disclose things like training data sources and capability limits to downstream AI system developers, and must respect copyright. For the most capable models, the rules also mandate stricter safety reviews to guard against misuse risks tied to chemical, biological, and nuclear domains, as well as systemic risks like loss of control and cyberattacks.
It's worth noting that none of these obligations are new — they've applied to newly released models since August 2025. What's changed is whether anyone can actually check. According to analysis from artificialintelligenceact.eu, enforcement isn't limited to the Commission acting unilaterally either: national market surveillance authorities can request that the Commission step in, and downstream developers who believe an underlying model they're using is non-compliant can file complaints directly.
The Deeper Read: What It Really Means When the Grace Period Closes
The easiest way to misread this moment is to assume "new rules just arrived." The more accurate framing is that the rules never changed — what changed is enforceability. Over the past year, GPAI providers have technically been operating under the Chapter V obligations already: disclosing training data as required, building out copyright-respecting mechanisms. But during that year, even if a provider fell short, regulators had no real investigative or financial teeth to act on it. That "in effect on paper, dormant in practice" status gave every player an implicit psychological cushion — the sense that nobody could actually come after them yet.
As of August 2, that cushion is gone. More importantly, this isn't an isolated shift in enforcement power — it's layered on top of a genuinely multi-channel oversight system: national regulators, downstream developer complaint channels, and a scientific expert panel are all now active simultaneously. That means a GPAI provider can be handling things fine at home and still get pulled into enforcement proceedings because of a complaint from a European downstream customer, or a proactive investigation by a national authority. The old mindset — compliance as a nice-to-have — has formally flipped, as of this date, into compliance as a survival baseline.
For any company doing business in the EU market, what really needs re-examining here is the mismatch between this news and the common perception of "AI compliance." Most companies' understanding of EU AI compliance still sits at the high-risk AI systems level — rules covering hiring, education, law enforcement, and immigration management don't formally apply until December 2027, which has given many the illusion that there's still time. But the GPAI enforcement regime that just took effect is an entirely separate track, already active, and it applies to anyone providing or integrating general-purpose AI model capabilities into the EU market — regardless of whether the end-use case counts as "high-risk." In other words, a company whose product doesn't come anywhere near the high-risk threshold can still be exposed to liability in theory, simply because its tech stack uses a regulated general-purpose model with gaps in its compliance documentation, content labeling, or risk assessment.
The more practical issue is that this regime's transparency requirements essentially demand auditable, documented evidence — not a verbal claim of compliance, but actual traceable records of training data provenance, risk assessment reports, and content labeling mechanisms. For teams accustomed to "build the business first, backfill compliance later," this requires a real shift in mindset: AI-related compliance infrastructure is no longer an elective that can be bolted on after launch — it needs to be built into the product design phase from day one.
In working with outbound trade clients, we often hear a version of: "let's get the product and customer acquisition running first, compliance can wait until we've scaled." This EU enforcement shift is a clear signal that mindset is becoming increasingly risky in the European market. For the clients we work with across Hong Kong, Indonesia, Malaysia, and Singapore, if any part of the business chain involves providing or integrating general-purpose AI capability for EU customers — whether in lead-generation tools, customer service systems, or the product itself — compliance documentation and risk assessment deserve the same attention as the acquisition channel itself; they're invisible infrastructure, but infrastructure nonetheless. Our own principle has always been that AI capability shouldn't be stacked on first with compliance patched in later — the boundaries need to be thought through at the design stage. What the EU just did, in effect, turned that principle from a best practice into a legal requirement.
Sources: MediaLaws / beam.ai / artificialintelligenceact.eu / European Commission
Was this article helpful?
Related Articles
Gemini 4 Neon: What Does a Completed AI Task Cost?
Gemini 4 Neon puts task speed and efficiency in focus. For businesses evaluating the model, the useful comparison includes retries, tool calls and the time people spend checking its work.
Read More
Claude Is Coming to Google Meet. The Work Could Start Before the Call Ends.
Anthropic plans to bring Claude into Google Meet so it can help draft plans during a call. The next question for businesses is how those decisions become tasks people actually follow up on.
Read More
Salesforce to Buy Cresta: What Can AI Get Done on a Customer Call?
Salesforce’s proposed Cresta acquisition would connect AI voice agents with Service Cloud. For customer service teams, the question is what an agent can actually get done before the caller hangs up.
Read More